


The Technical Landscape of the Lapsus$ Intrusion
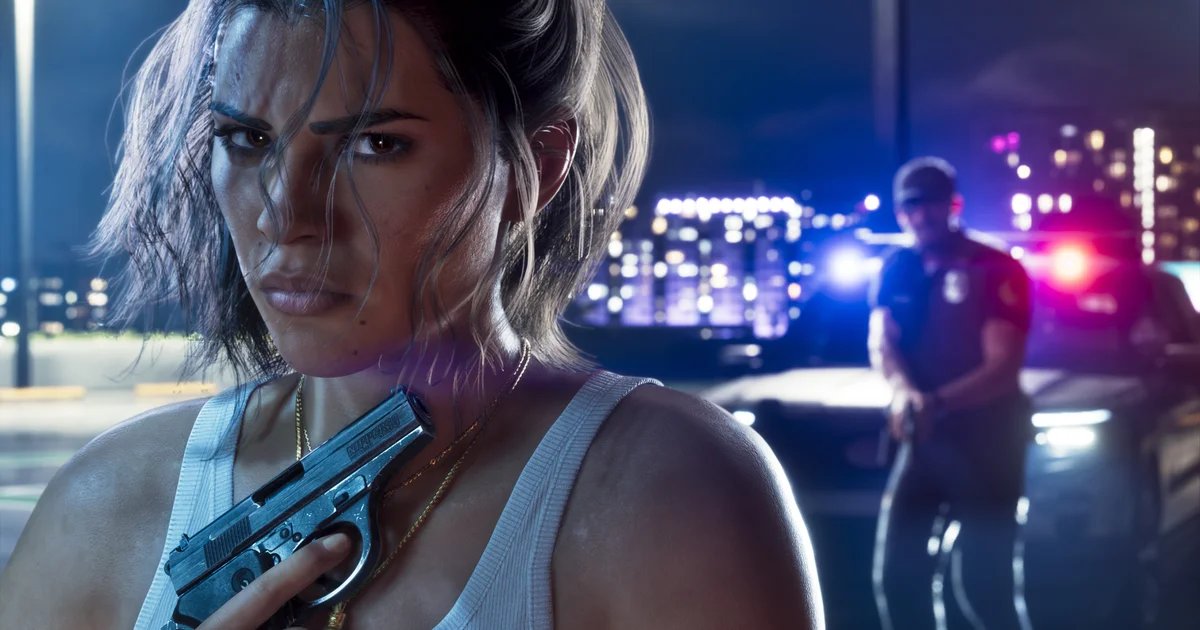
The digital security landscape remains under constant scrutiny as the legal proceedings against Arion Kurtaj, a central figure in the Lapsus$ cybercrime collective, reach a definitive conclusion. Kurtaj, whose activities gained international notoriety through the unauthorized distribution of Grand Theft Auto VI development footage, has officially entered a guilty plea following a prolonged series of judicial evaluations. His actions provide a case study in how unsophisticated hardware setups can be leveraged to bypass robust corporate security protocols, highlighting significant vulnerabilities in modern identity management and network access control.
The investigation conducted by the Crown Prosecution Service (CPS) revealed a persistent pattern of unauthorized access beginning in late 2021. Kurtaj’s initial operations targeted BT/EE, specifically focusing on the manipulation of Subscriber Identity Module (SIM) authentication. By performing unauthorized SIM swaps, the attacker successfully intercepted multi-factor authentication (MFA) requests, effectively gaining control over privileged accounts. This method serves as a reminder that even when complex encryption is in place, the weakest point of a secure system is frequently the reliance on telecommunications infrastructure for identity verification.
Methodologies Behind the Breach
Perhaps the most striking technical aspect of Kurtaj’s campaign was the minimal infrastructure utilized to sustain the attacks. During the period he was housed in a hotel under protective custody, he maintained his illicit activities using only a mobile phone, a hotel television’s wireless connection, and an Amazon Firestick. This minimalist approach suggests that the technical hurdle for high-level corporate espionage has been lowered significantly, provided the attacker possesses a deep understanding of social engineering and the weaknesses of cloud-based internal portals.
By gaining access to internal communication tools and development environments—such as Slack and Jira—Kurtaj was able to navigate corporate networks with the authority of a legitimate employee. Once inside these environments, the lack of sufficient internal network segmentation allowed for lateral movement. The ability to exfiltrate proprietary data, including nearly 100 clips of unreleased Grand Theft Auto VI gameplay, demonstrates that once an attacker bypasses the perimeter, they can gain wide-ranging visibility into sensitive development lifecycles.
Impact on Corporate Security Paradigms
The ripple effects of the Lapsus$ hacks have prompted a significant re-evaluation of zero-trust architecture among major technology firms. The ease with which the group traversed the infrastructure of companies like Rockstar Games, Uber, and Revolut underscores the necessity of moving beyond simple password and SMS-based verification. Organizations are now increasingly shifting toward hardware-based security keys and more rigorous identity and access management (IAM) frameworks that verify context, device health, and user behavior rather than relying solely on credentials.
Furthermore, the case illustrates the risks associated with remote development environments. As companies maintain more distributed workforces, the perimeter of the network has effectively shifted to the endpoint device. When those devices are not managed with strict adherence to security policies, or when authentication mechanisms are susceptible to interception, the risk of data exfiltration rises exponentially. The Lapsus$ incidents serve as a catalyst for tighter integration of Endpoint Detection and Response (EDR) tools designed to flag anomalous login activity, such as concurrent sessions from disparate geographic locations.
Navigating the Legal and Institutional Response
The judicial history of this case has been as complex as the technical maneuvers involved. Initially, Kurtaj was committed to a secure hospital setting due to professional assessments regarding his autism and mental health status. However, a reassessment in early 2024 determined that he was fit to stand trial, resulting in his transfer to a standard penal facility. This pivot in the legal response highlights the ongoing challenge of managing cybercrime cases involving individuals whose psychological profiles complicate traditional punishment frameworks.
As the sentencing date of November 23rd approaches, the tech industry is observing the final chapter of a saga that began with a series of high-profile data leaks. The juxtaposition of the sentencing date with the upcoming release of Grand Theft Auto VI is not merely symbolic; it represents the conclusion of a significant disruption to one of the most anticipated product launches in the history of interactive entertainment.
The Future of Digital Forensics and Incident Response
The evolution of the Lapsus$ case provides critical insights into the future of incident response. It demonstrates that the most effective defenses against such actors are not necessarily more expensive, but rather more restrictive regarding authentication and internal authorization. Real-time monitoring of developer environments, combined with restricted access to sensitive source code repositories, acts as a primary deterrent against the unauthorized exfiltration of intellectual property.
Moving forward, the industry must prioritize the hardening of telecommunications-based authentication and the adoption of more resilient identity verification technologies. The lessons learned from this breach have already begun to influence how organizations handle their internal security audits. By closing the gaps that allowed mobile-based manipulation and unauthorized network access, firms hope to mitigate the success of future actors who seek to exploit similar pathways. The technical legacy of the Lapsus$ group will likely be defined by the industry-wide move toward more comprehensive internal defense strategies, ensuring that hardware limitations—such as those present in a standard hotel television set—can no longer provide the entry point for large-scale corporate data breaches.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News