






A Record-Breaking Volume of Security Updates
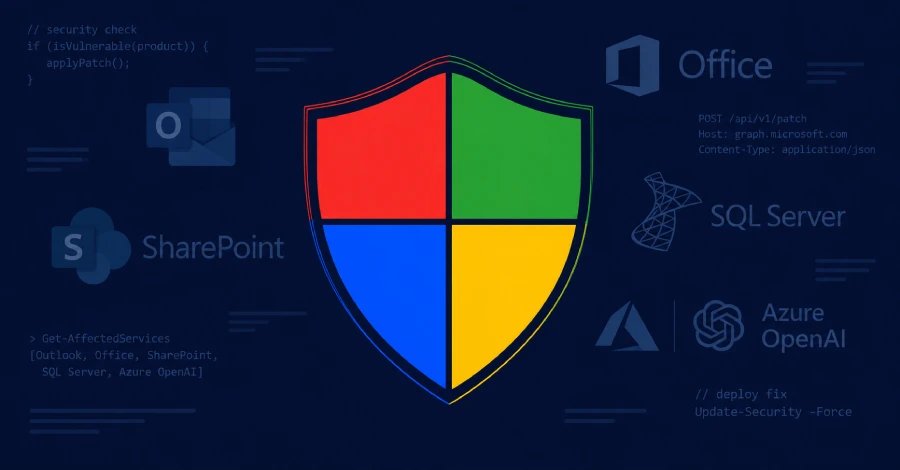
Microsoft has issued a massive security update cycle for November 2026, addressing a staggering 1,259 vulnerabilities across its extensive software ecosystem. This release marks the second consecutive month in which the volume of patched flaws has exceeded the 1,000-mark, highlighting an ongoing trend of high-frequency security maintenance for the Redmond giant. With these latest fixes, the total number of Common Vulnerabilities and Exposures (CVEs) addressed by Microsoft in 2026 has surpassed 5,100.
The breadth of these updates is significant, covering critical components such as Windows (726 flaws), Office (174), Developer Tools (61), SQL Server (59), and SharePoint Server (27). Additionally, the patch set incorporates 165 CVE identifiers that originate from non-Microsoft sources, underscoring the interconnected nature of modern software supply chains. The vast majority of these issues pertain to elevation of privilege, followed by various remote code execution and information disclosure bugs.
The Active Threat: CVE-2026-124194
Among the laundry list of security concerns, the most pressing is CVE-2026-124194, a vulnerability affecting Microsoft Outlook. While officially categorized with a Moderate severity rating and a CVSS score of 6.5, the flaw has been confirmed as actively exploited in the wild. The vulnerability stems from a failure in the product’s user interface to properly alert users when they are performing potentially unsafe actions, specifically regarding the handling of network content.
An attacker can exploit this weakness by crafting a malicious message file. When a user opens this file, Outlook fails to present the standard external-content warning. This allows the application to connect to an attacker-controlled network location automatically. During this handshake, the client can leak sensitive authentication information, most notably NTLMv2 hashes. Once captured, these hashes allow an adversary to perform relay attacks or offline brute-force attempts to impersonate the victim, thereby gaining unauthorized access to the user’s account, sensitive data, and potentially wider network infrastructure.
Industry Concerns and Strategic Impact
Security experts are sounding the alarm regarding the misclassification of this Outlook flaw. By allowing identity theft through a single, seemingly innocuous file opening, the vulnerability carries a weight that exceeds its “Moderate” label. The ubiquity of Outlook within corporate environments makes this an ideal entry point for malicious actors seeking to move laterally across an organization’s systems.
The threat is deemed severe enough that the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added the vulnerability to its Known Exploited Vulnerabilities (KEV) catalog. This designation mandates that all federal civilian agencies implement the provided patches by November 24, 2026. Because successful exploitation relies on a combination of network connectivity and user interaction, security teams are advised to prioritize user awareness in tandem with aggressive patch deployment.
Broad Systemic Vulnerabilities Beyond Outlook
The November patch cycle is not limited to client-side application flaws; it also addresses significant infrastructure and service-level vulnerabilities. Among the high-impact issues being resolved are several remote code execution (RCE) flaws found in Windows Search, the Lightweight Directory Access Protocol (LDAP) implementation, and Windows Schannel. These vulnerabilities are particularly dangerous as they can allow unauthorized individuals to execute arbitrary code on a target machine, often without prior authentication.
Further complications were identified in the Windows Virtual Filtering Platform and the Windows Xbox Live Networking Service, both of which received critical attention this month. Additionally, a notable privilege escalation flaw was discovered in Azure OpenAI (CVE-2026-119990), highlighting the expanding attack surface as organizations increasingly integrate generative AI services into their operational workflows. These updates serve as a reminder that vulnerabilities can exist anywhere within the technology stack, from legacy networking services to modern cloud-hosted artificial intelligence tools.
Managing Patch Fatigue
The relentless pace of these security updates has created considerable operational pressure for information technology and cybersecurity departments. Many organizations are struggling to keep up with the constant demand for verification and deployment, leading to a state of sustained fatigue. Industry analysts emphasize the need for a disciplined, risk-based approach to vulnerability management rather than a reactive “firefighting” mindset.
For organizations overwhelmed by the volume of patches, the consensus is to implement a strategic prioritization model. Security leaders should focus first on internet-facing assets that have existing exploits associated with them, as these present the highest immediate risk. Following that, firms should address vulnerabilities for which internal prerequisites for exploitation—such as administrative privileges or specific network configurations—are already met. By filtering out patches for components that are either not in use or not reachable in their specific environment, IT teams can maintain a robust security posture without succumbing to burnout from the sheer number of security advisories.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News


