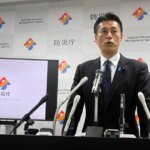
TOKYO — GMO Internet Group, a prominent Japanese technology firm, has publicly acknowledged a significant security failure following a string of devastating cyberattacks. During a somber news conference held in Tokyo on Monday, top leadership, led by CEO Masatoshi Kumagai, offered deep apologies as the company grappled with the fallout of a massive data breach involving its “Onamae.com Desktop Cloud” service.
The incident, which reportedly impacted over 26,000 cases, resulted in unauthorized account access and the execution of unauthorized financial transactions across dozens of securities firms and corporate clients. As the Japanese tech giant attempts to restore its reputation, the breach has sparked a broader debate regarding the state of cybersecurity infrastructure in Japan.
## A Failure of Internal Oversight
During the briefing, CEO Masatoshi Kumagai admitted that the company had received internal warnings regarding systemic vulnerabilities in its security architecture. Despite these early red flags, the necessary defensive measures were not implemented in time to stave off the attack.
“I offer my deepest felt apologies,” Kumagai stated, visibly emotional as he addressed the assembly. The CEO, who founded the firm in 1991, also addressed public backlash regarding his recent social media activity, specifically a photo of him smiling that had circulated after the breach became public. To demonstrate accountability, Kumagai announced a 30% reduction in his salary for the next three months, with other senior executives also accepting smaller pay cuts.
Beyond symbolic gestures, GMO has committed to a complete overhaul of its security protocols and has pledged to provide financial compensation for all verified losses. As a gesture of goodwill, the company is offering a 5,000 yen (approximately $30) payment to all affected customers.
## Bounty Programs and the Ransomware Threat
GMO confirmed that the attackers utilized ransomware to cripple operations. The company opted not to pay the ransom demand. Instead, it has taken a proactive stance by launching a “GMO Cybercrime Bounty” website. The platform, which supports English, Japanese, and Chinese, offers a $1 million reward for actionable intelligence leading to the identification and arrest of the perpetrators. According to the company, over 400 tips have been submitted since the program’s inception last week.
The incident is particularly sensitive given GMO’s role in the tech ecosystem. As a provider of cybersecurity, online marketing, and infrastructure support for AI and robotics, the company is expected to uphold the highest standards of digital protection. The breach, coupled with the recent record-breaking $6 billion cryptocurrency heist linked to a North Korean hacking unit, has underscored an urgent need for more robust digital defenses across Japan’s corporate and government sectors.
## Industry Impact and Regulatory Scrutiny
The fallout has been immediate for GMO’s market position. Shares of the company have fallen by 17.5% year-to-date, reflecting investor anxiety regarding the firm’s long-term financial stability following the attack. While the government has not formally commented on the specific GMO case, Prime Minister Sanae Takaichi has recently signaled that Japan will aggressively bolster its national cybersecurity posture to better address these growing threats.
As the industry moves toward deeper integration with artificial intelligence and automated cloud infrastructures, experts warn that the “low sense of crisis” that has persisted in Japanese cybersecurity circles must be discarded. For GMO, the path to recovery involves not just technical remediation—switching to a new, more secure system—but also rebuilding the trust of its clients in an increasingly volatile digital landscape. The company remains under intense scrutiny as it works to quantify the total impact of the breach on its fiscal health.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News