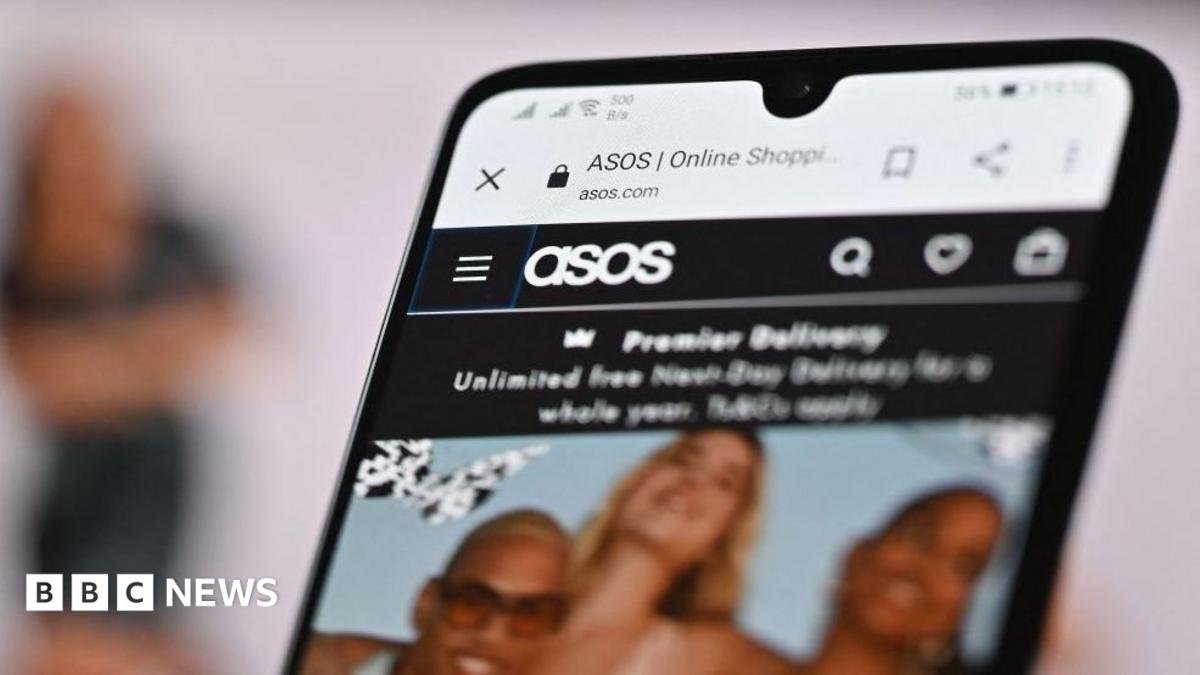
ASOS customers across the globe were met with a startling disruption this morning as a mysterious, high-profile extortion message appeared directly within the retailer’s official mobile application. The incident has triggered widespread confusion and alarm, as the message appears to be a formal demand directed at the company’s internal IT department and data protection officer (DPO).
The unusual notification claims that a group of hackers, identifying themselves as “Xuanye Group,” has “fully compromised the Snowflake instance” associated with the fashion giant. Snowflake, a cloud-based data storage and analytics provider, has been the focal point of several high-profile security breaches in recent years, including major incidents involving Ticketmaster and Santander.
While it remains unclear whether ASOS utilizes Snowflake for its data operations, or what specific information—if any—might have been exposed, the delivery method of the message has security experts deeply concerned. Rather than following the standard industry practice of contacting a company privately to negotiate a ransom, the attackers chose to broadcast their breach directly to thousands of users through the company’s own push notification system.
Dan Bird, a lead researcher at cybersecurity firm Horizon3, notes that this method suggests a much broader and more dangerous level of system access than the hackers initially disclosed.
“Sending a push notification to ASOS’s app users would require access to the company’s notification system, which is separate from the Snowflake data platform the attackers claim to have compromised,” Bird explained. “If both claims hold up, it suggests the attackers got hold of credentials that opened more than one door. This is not a simple data leak; it indicates an active, ongoing breach of the company’s internal infrastructure.”
The group behind the intrusion, Xuanye Group, appears to be newly formed. Their Telegram channel, which was linked directly within the pop-up notification, was created only today and has posted fewer than a dozen times. The brevity and public nature of their communication are highly atypical for modern cyber extortionists, who usually prefer to operate in the shadows to secure a quiet financial payout.
The public display of the ransom note has led to a flurry of activity on social media, with ASOS users posting screenshots of the warning and questioning the safety of their personal and financial data. ASOS has yet to provide a detailed statement regarding the scope of the breach or the nature of the systems involved.
As the situation develops, industry experts are warning users to remain vigilant. The tactics employed by Xuanye Group represent a shift toward “public-facing” extortion, a strategy designed to maximize embarrassment and panic, thereby placing immense pressure on the victimized company to address the ransom demands immediately. For now, the breadth of the compromise remains the subject of intense investigation by security analysts.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News