The Impending Shift Toward Regulatory Synergy in India
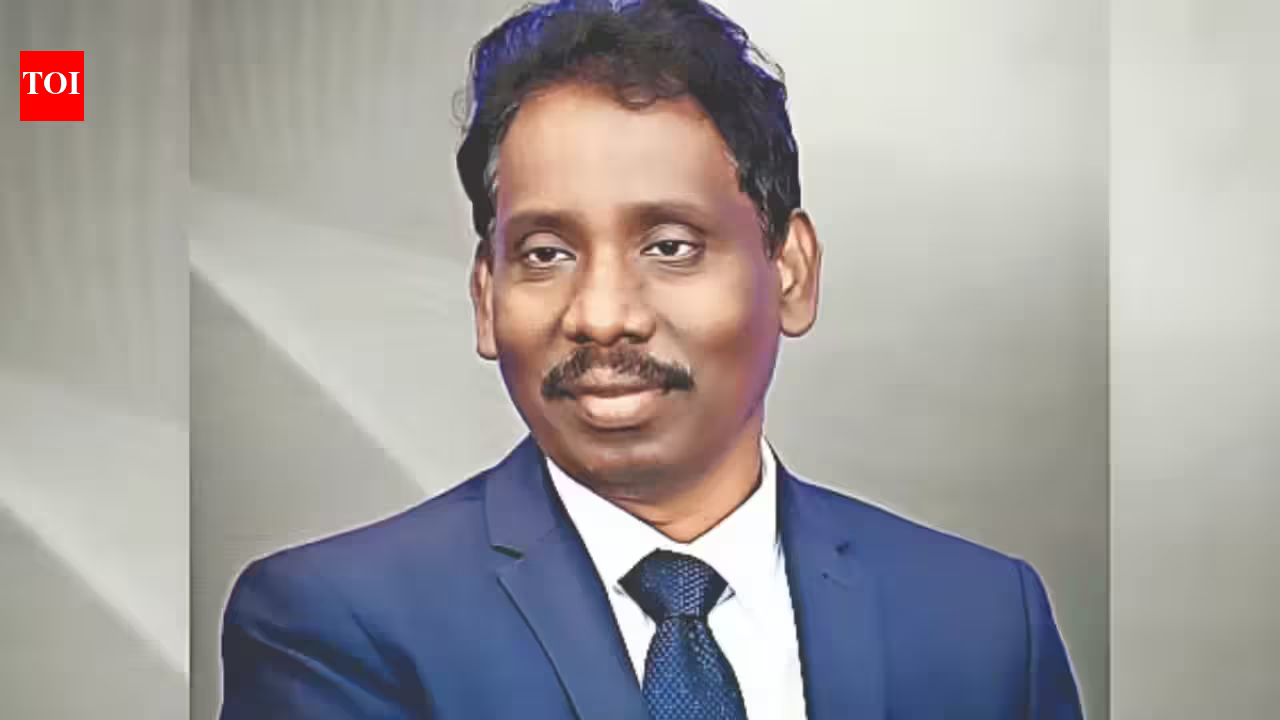
The Indian financial landscape is currently witnessing a period of rapid evolution, characterized by digital transformation, the integration of diverse financial services, and a blurring of lines between traditional banking, insurance, and asset management. As financial entities expand their service portfolios, the risk profile of these institutions has become increasingly complex. Deputy Governor of the Reserve Bank of India (RBI), SC Murmu, recently highlighted a critical challenge stemming from this evolution: the presence of overlapping regulatory jurisdictions. In his address at the Gatekeepers of Governance 2026 event, Murmu underscored the necessity for heightened coordination among India’s primary financial regulators to manage systemic risks that no longer respect institutional silos.
For decades, the regulatory framework in India was designed around specialized oversight. The RBI managed banking and monetary policy; the Securities and Exchange Board of India (SEBI) looked after market integrity; and the Insurance Regulatory and Development Authority of India (IRDAI) monitored insurance operations. However, the rise of the financial supermarket model, where banks act as distributors for insurance and mutual fund products, has fundamentally altered this arrangement. When a consumer faces mis-selling of a financial product at a bank branch, the issue occupies a grey area that concerns the mandates of all three regulators. Murmu’s call for closer cooperation signals a shift toward a more holistic, interconnected approach to financial governance in India.
Addressing the Challenges of Integrated Financial Services
The integration of financial services has created a scenario where regulatory mandates intersect far more frequently than they did in the past. Banks, which have historically served as the bedrock of the Indian economy, are now significant players in the distribution of investment products. This diversification is beneficial for customer access but complicates the enforcement of compliance. For instance, when a bank engages in the sale of complex insurance policies or market-linked investment products, it must adhere to RBI’s prudential norms, SEBI’s disclosure requirements for distributors, and IRDAI’s consumer protection standards.
This layering of regulations creates an environment where, despite rigorous oversight, systemic gaps can emerge. Mis-selling remains a persistent concern in the retail financial sector, and when the distribution channel is a regulated bank, the responsibility for oversight becomes fragmented. Murmu’s proposition implies that the era of regulators operating in relative isolation is coming to an end. Instead, there is a clear imperative for joint enforcement mechanisms and unified disclosure standards that protect the end-consumer regardless of which license the selling entity holds. By streamlining these mandates, regulators can reduce the compliance burden on financial institutions while simultaneously increasing the effectiveness of consumer protection measures.
Cybersecurity as a Multi-Regulatory Frontier
Perhaps the most pressing area requiring inter-regulatory coordination is the digital ecosystem. In an era of interconnected financial systems, a cyberattack on a single entity—whether a bank, a brokerage, or a national payment gateway—can trigger a domino effect across the entire financial architecture. The interconnectedness of modern digital banking means that a technical failure or a security breach in a bank’s infrastructure can rapidly compromise mutual fund platforms or insurance databases.
The current challenge, as noted by Murmu, is that while each regulator has its own set of cybersecurity guidelines, there is a lack of a unified national standard for cyber resilience that covers all financial sectors. A bank’s cyber defenses might meet RBI standards, but the third-party providers they integrate with may fall under a different set of security expectations. Establishing common, high-level cybersecurity protocols that are enforced uniformly across the financial sector is essential. This would involve real-time information sharing between regulators during a crisis, ensuring that a breach identified in one market infrastructure is immediately communicated and addressed across the board to prevent systemic contagion.
Navigating Related-Party Transactions and Prudential Norms
Corporate governance, particularly the issue of related-party transactions, serves as a prime example of where jurisdictional overlaps are most pronounced. For a listed bank in India, the oversight structure is multifaceted. It must comply with RBI’s strict guidelines on related-party lending to ensure that bank capital is not diverted to group companies at the cost of depositors. Simultaneously, it must satisfy SEBI’s listing regulations, which mandate rigorous disclosures and shareholder approvals for such transactions.
This creates a high compliance cost and, at times, inconsistent interpretations of rules. Murmu suggests that instead of each regulator adding layers of new rules to cover these gaps, there must be a consensus-based approach to defining the parameters of acceptable behavior. By communicating expectations more clearly and harmonizing the definitions used across the financial sector, regulators can create a more predictable environment. This shift would allow financial institutions to focus on transparency and operational efficiency rather than navigating a maze of potentially conflicting regulatory expectations.
Shifting from Proliferation of Rules to Principled Oversight
A recurring theme in the discourse on modern financial regulation is the risk of “regulatory fatigue”—a condition where the sheer volume of rules begins to hamper business innovation and economic growth. Murmu’s guidance suggests that the focus should shift away from attempting to keep pace with every new industry development through the constant introduction of new rules. In a rapidly changing technological climate, a rule-heavy approach can quickly become obsolete.
Instead, the future of Indian regulation lies in clear communication of expectations and a focus on core principles of governance and risk management. By clearly stating what is expected of boards of directors—particularly regarding their understanding of AI-driven algorithmic risks and systemic vulnerabilities—regulators can foster a culture of compliance that is self-regulating. When boards are well-informed and the expectations are consistent across the RBI, SEBI, and IRDAI, the need for exhaustive, granular rulemaking diminishes. This strategic shift represents a move toward a more mature, risk-based regulatory environment that supports, rather than stifles, the competitive vitality of the Indian financial sector.
The Road Ahead for Coordinated Financial Governance
The road to closer regulatory coordination in India is not without its hurdles. It requires significant technical and institutional integration. Shared databases, unified cyber-incident response teams, and joint monitoring of large financial conglomerates will be necessary to turn this vision into reality. However, the benefits of such an approach are clear: a more stable financial system, better consumer protection, and a streamlined regulatory environment that reduces the cost of doing business.
As India continues to solidify its position as a global financial hub, the capability of its regulators to act in concert will define its long-term resilience. The proactive stance taken by the RBI, as voiced by Deputy Governor Murmu, is a necessary step toward aligning the regulatory framework with the realities of a modern, digitized economy. By prioritizing coordination over siloed control, India’s financial gatekeepers can ensure that the sector remains robust enough to withstand future shocks while providing the transparency and security that stakeholders and customers demand in the 21st century.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News