The Hidden Legacy of Abandoned Streaming Software
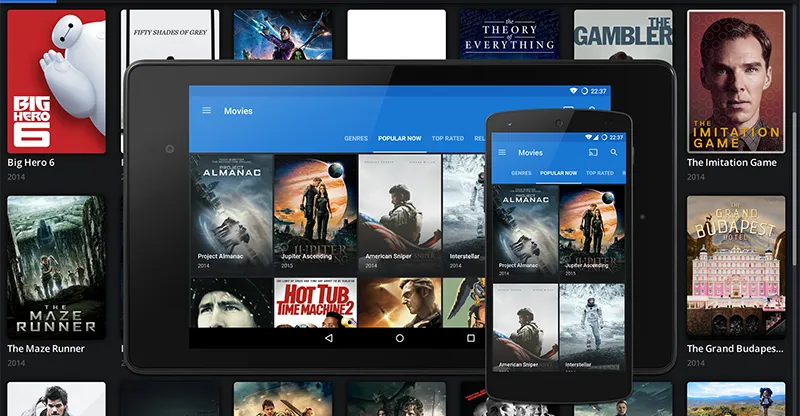
In the mid-2010s, a software project known as Popcorn Time revolutionized how users engaged with torrent-based content. By providing a streamlined, intuitive interface that obscured the complexity of peer-to-peer file sharing, it earned the nickname “the Netflix of piracy.” While the project effectively withered away under immense legal pressure and developer burnout, the digital architecture remains embedded on millions of consumer devices. Recent investigations conducted by security researchers at Eye Security have uncovered that a specific fork of the application, marketed as “Time4Popcorn,” remains a significant security liability due to its persistent and insecure update mechanism.
For years, these legacy installations have continued to operate in the background. Despite the application’s lack of functional service, the internal updater continues to poll external, long-abandoned domains to check for new versions. This behavior creates a persistent vulnerability, as the traffic is transmitted over unencrypted HTTP, leaving the update process open to interception and exploitation by malicious actors.
Technical Vulnerabilities and the Threat of Botnet Recruitment
The security risk inherent in these installations stems from how the software handles updates. Researchers discovered that the updater possesses the capacity to download and execute arbitrary code with full system privileges. In the realm of cybersecurity, this is a critical flaw. Because the application was designed to bypass traditional security hurdles to ensure seamless streaming, it granted itself extensive access to the host operating system.
If a malicious entity were to seize control of the expired domains that the updater queries, they could effectively push a malicious payload to every active installation of the software. This creates a massive, ready-made botnet. By hijacking the update flow, an attacker could distribute ransomware, deploy keyloggers for credential theft, or integrate these devices into a distributed denial-of-service (DDoS) network. Furthermore, because the updater uses unencrypted HTTP, attackers could execute man-in-the-middle attacks to inject their own software, even without direct control over the original domain infrastructure. The potential for large-scale surveillance is equally concerning, as the update pings inherently identify the IP addresses and device types of every active user.
The Ethics of a White-Hat Intervention
Faced with a potential security catastrophe involving millions of globally distributed endpoints, the team at Eye Security made the decision to intervene. By registering one of the abandoned domains that the software was programmed to check, the researchers were able to broadcast their own update signal to the connected client devices. This intervention was not designed to steal data or disrupt the machines; rather, it functioned as a “kill switch.”
The update directed the software to permanently disable the vulnerable background service. On Windows machines, the update interacted with the Service Control Manager to cease and terminate the service, while on macOS, it triggered a shell script designed to prevent the update process from initiating. This method of remediation raises pertinent questions regarding software ownership and unauthorized access. However, the researchers argued that doing nothing was not a viable path forward, as the status quo was already facilitating a massive security hazard. By neutralizing the updater, the researchers effectively severed the command-and-control capabilities that an adversary could have leveraged.
Challenges in Patching Legacy Software
The remediation process was not without its technical difficulties. After the researchers uploaded their neutralizing patch to VirusTotal—a standard procedure for verifying the safety of code—security vendors identified the patch as a threat. The automated systems of these security companies, detecting an unknown file modifying system services and files, flagged the update as malware. This resulted in a paradoxical situation where the very tools designed to protect systems were preventing the deployment of a security fix for a critical vulnerability.
To circumvent this, the team had to refine their approach to ensure the patch would be accepted by security scanners while still successfully executing its task on target machines. This incident highlights the inherent friction between legitimate security interventions and the automated defensive protocols that govern modern endpoint security. It also underscores the sheer scale of the operation, with the researchers reporting that they sent over two million update packages before ceasing their efforts.
The Role of Shadowserver and Long-Term Security
As the operation concluded in March, the researchers transferred the domains used in their intervention to the Shadowserver Foundation, a non-profit organization dedicated to enhancing the security of the internet. This transfer ensures that the infrastructure remains in responsible hands, preventing future bad actors from re-registering the domains and reclaiming control over the dormant botnet.
The broader lesson from the Popcorn Time incident is the danger of “zombie” software. When developers abandon a project, the infrastructure—such as domain names and server certificates—often expires. If the software is not programmed to handle these failures gracefully or to verify updates via secure cryptographic signatures, it becomes a permanent liability. As devices continue to proliferate in the Internet of Things era, the lifecycle management of software remains a significant hurdle. Users are often unaware of the background services running on their machines, highlighting a persistent need for better transparency and automated maintenance protocols to ensure that unused applications do not become the primary vehicle for future cyberattacks.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News