

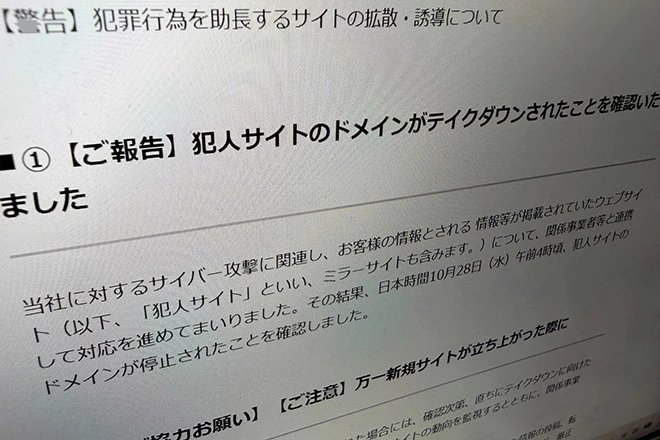
TOKYO — In a significant escalation in the battle against cyber-extortionists, GMO Internet Inc. announced on October 28 that the malicious domain used by hackers to leak stolen customer data has been forced offline. The move comes after the company flatly rejected a $50 million ransom demand, triggering a series of retaliatory data dumps.
The extortion site, which had begun publishing the names, addresses, and account details of GMO customers on October 27, was rendered inaccessible following the suspension of its domain by the registrar. According to ICANN records, both the primary site and an identified mirror site were taken down after reports indicated they were hosted by an overseas provider. A social media user on X claimed to have alerted the hosting provider to the site’s illegal activity, leading to a pledge from the provider to take swift action.
The cyberattack, which targeted the company’s “Onamae.com Desktop Cloud” service—frequently used for automated forex trading—resulted in reports of unauthorized transactions within customer accounts. The perpetrators had threatened a campaign of continued information leaks and ransomware attacks unless the $50 million payout was met. GMO Internet Group has maintained a firm stance, declaring that it will not negotiate with or pay the attackers.
In response to the breach, the company has launched a multi-pronged counter-offensive. GMO is now offering a bounty of up to $1 million for information leading to the identification or arrest of the individuals behind the operation. The company is actively soliciting tips, including details on server infrastructures and cryptocurrency transaction trails, with a dedicated channel open for global reports as of noon on October 28.
“We will immediately seek the takedown of any replacement site,” a company spokesperson stated, while simultaneously warning the public to refrain from accessing the attackers’ domains or circulating leaked data.
To mitigate the fallout for its user base, GMO Internet Group also unveiled a comprehensive relief package. Beyond an initial 5,000-yen flat payment and full coverage for losses stemming from unauthorized account transactions, the company is issuing tiered compensation based on the sensitivity of the leaked data: 10,000 yen for basic contact information, 15,000 yen for authentication or trading credentials, and 25,000 yen for highly sensitive private data.
As the investigation continues, the tech giant remains under intense pressure to secure its infrastructure and restore client confidence. The company confirmed on October 27 that while some data was indeed leaked, it continues to monitor the dark web and other venues for further unauthorized activity. The incident highlights the growing risks faced by financial technology service providers as they navigate increasingly sophisticated global cyber threats.
(Compiled from reports by Ryo Sanada and Azusa Ushio.)
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News