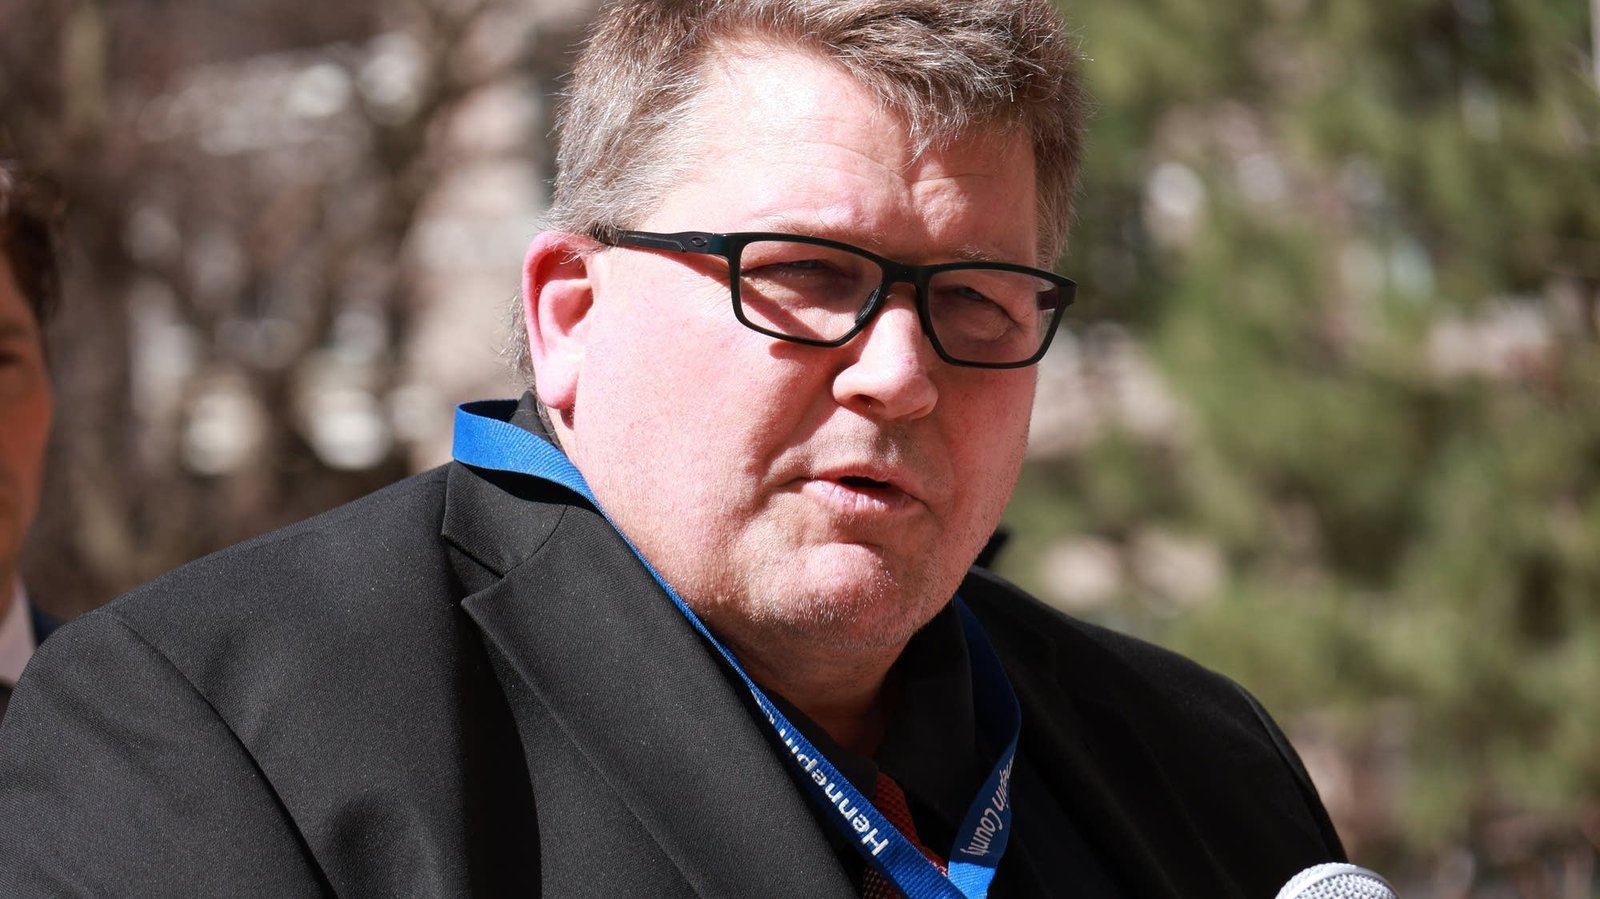
Hennepin County has officially shuttered its $2 million Small Business Recovery Fund after a massive surge of suspicious activity brought the initiative to a standstill. Launched in March with the intent of providing financial relief to local enterprises impacted by the disruptions of “Operation Metro Surge,” the program was intended to be a lifeline for the community. Instead, county officials discovered that nearly two-thirds of the applications submitted for funding were flagged for potential fraud, forcing an immediate halt to the program.
## The Digital Footprint of Modern Fraud
The collapse of the Small Business Recovery Fund highlights a growing crisis in the administration of public financial programs: the vulnerability of application portals to sophisticated, automated fraud. Hennepin County Commissioner Jeffrey Lunde recently addressed the situation in an interview with MPR News, emphasizing that the sheer volume of fraudulent submissions—numbering over 200—rendered the verification process unsustainable.
While the county has not detailed the exact technical methods used by the bad actors, experts in the cybersecurity field have noted that public funding portals are increasingly targeted by AI-driven bot networks. These systems can synthesize legitimate-looking business data, generate convincing tax documents, and submit thousands of applications in a matter of seconds. In the age of generative AI, the barrier to entry for digital identity theft and synthetic fraud has never been lower, turning well-intentioned relief programs into primary targets for organized cybercrime.
## AI and the Future of Verification
The failure of this fund underscores the urgent need for better technological oversight in government distribution channels. As local and federal agencies roll out digital grants, the integration of advanced identity verification (IDV) tools has become a critical necessity. Modern fraud-detection software—often powered by machine learning algorithms—is capable of cross-referencing public tax records, business registrations, and geolocation data in real-time.
Tech industry leaders argue that moving forward, government agencies must treat application portals with the same security rigor as banking or fintech infrastructure. By implementing multi-factor authentication (MFA) and AI-based behavioral analysis, administrators can identify “bot-like” patterns before a submission ever reaches a human reviewer. Without these digital safeguards, public initiatives intended to uplift small businesses are susceptible to being drained by malicious actors before they reach those who truly need help.
## The Human Cost of Automated Attacks
For the legitimate small business owners who were waiting on these funds to pay rent or cover payroll, the shutdown is a significant blow. Commissioner Lunde acknowledged the frustration felt by local entrepreneurs who played by the rules only to see the fund collapse under the weight of external attacks.
The incident serves as a stark reminder that the digital transformation of government services requires a parallel transformation in security strategy. As Hennepin County pivots to re-evaluate how it distributes disaster recovery and business support funds, the broader public sector is watching. The challenge lies in balancing accessibility with verification; while the goal is to get money to businesses quickly, the “move fast and break things” philosophy often favored in the tech sector can lead to catastrophic losses when applied to sensitive public tax dollars.
As the county looks toward future programs, officials are expected to explore more robust verification partnerships with tech firms and cybersecurity consultants. For now, the shuttering of the Small Business Recovery Fund stands as a cautionary tale of how the intersection of public funding and digital vulnerability can disrupt the very communities they were designed to protect.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News