The Evolving Landscape of Digital Banking Liability in India
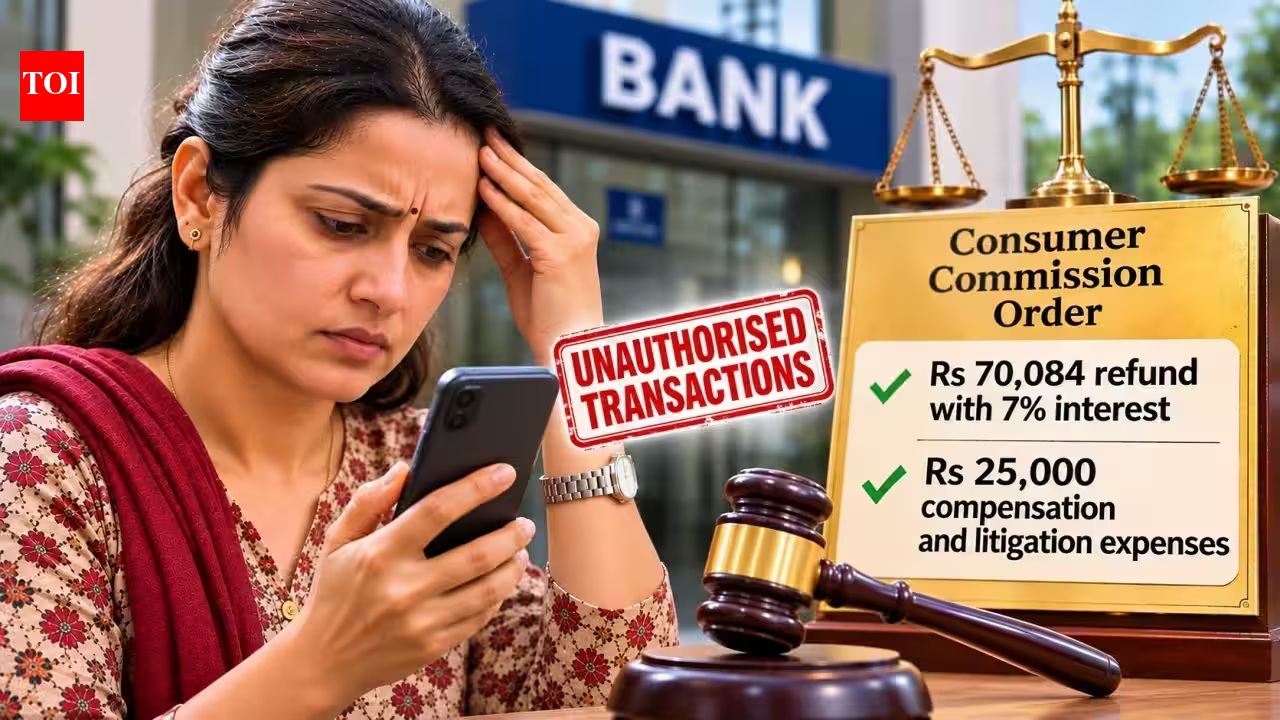
The rapid digitization of the Indian economy, accelerated by the Unified Payments Interface (UPI) and the proliferation of digital wallets, has brought significant convenience to millions of consumers. However, this shift has also introduced systemic vulnerabilities. As digital transactions become the primary mode of exchange, instances of unauthorized debits and financial fraud have surged, putting a strain on the traditional relationship between banks and their customers. The recent judgment by the Delhi Consumer Disputes Redressal Commission involving a decade-long legal battle serves as a critical reminder that the burden of securing digital infrastructure lies primarily with financial institutions, not just the account holders.
This case, where a consumer successfully recouped funds lost in unauthorized transactions, highlights the pivotal role of the Reserve Bank of India’s (RBI) guidelines in shaping consumer protection. For many years, banks often relied on the defense that a compromised One-Time Password (OTP) or exposed card details constituted “customer negligence.” This blanket denial often left victims without recourse. The commission’s ruling signals a departure from this practice, emphasizing that banks must provide concrete evidence of negligence to shift liability onto the customer.
Understanding the RBI Framework for Customer Protection
The foundation of the commission’s verdict lies in the RBI circular titled “Customer Protection—Limiting Liability of Customers in Unauthorized Electronic Banking Transactions.” This policy framework is designed to balance the interests of a digital-first economy with the necessity of consumer safety. According to these guidelines, customers are entitled to zero liability if they report unauthorized transactions within a specified time frame, especially when the breach is attributed to third-party fraud or systemic deficiencies within the bank’s own security layer.
In the Indian context, the distinction between “contributory negligence” and “systemic failure” is paramount. Banks are mandated to implement robust multi-factor authentication and monitoring systems. When a transaction occurs that deviates from a user’s typical profile or when security alerts fail to trigger—as was the case with the Delhi-based consumer who did not receive timely SMS notifications—the bank’s failure to provide these auxiliary security services acts as a form of deficiency in service. The ruling clarifies that a bank cannot merely cite the sanctity of the OTP process to insulate itself from liability if it cannot prove that the customer acted with gross negligence.
The Burden of Proof and Legal Accountability
A significant aspect of this case was the bank’s failure to substantiate its claims. During the legal proceedings, the bank asserted that the leakage of banking credentials was entirely the fault of the account holder. However, the commission held that under the current regulatory framework, the onus of establishing customer liability rests with the institution. In the absence of forensic evidence or logs proving that the customer inadvertently shared sensitive information, the bank’s claims remained speculative.
This shift in the burden of proof is a crucial development for Indian consumers. Historically, individual account holders were disadvantaged by the sheer lack of technical information available to them regarding how a server-side breach or an API vulnerability might occur. By demanding that banks provide documented proof of negligence, the Consumer Commission has effectively raised the bar for financial institutions. For the Indian banking sector, this necessitates a more transparent reporting mechanism. Banks must now maintain granular audit trails of every transaction to justify why they believe a customer was responsible for a security compromise.
Operational Deficiencies and the Impact on Consumer Rights
The case also sheds light on the collateral damage caused by unauthorized transactions. The consumer reported not just the loss of the principal amount, but also the ripple effects: ECS penalty charges, the lapsing of a life insurance policy, and the impact on mutual fund investments. These cascading financial damages represent a genuine “deficiency in service” because the bank’s inability to secure the account directly triggered a chain of adverse events for the customer.
For Indian business entities, particularly fintechs and traditional banks, this highlights a broader operational risk. The reputational and legal costs of a decade-long litigation process far outweigh the cost of implementing a robust, proactive fraud-detection system. When banks fail to provide real-time alerts or ignore customer communications regarding suspected fraud, they leave themselves vulnerable to compensation claims that exceed the value of the unauthorized transactions themselves. In this specific case, the compensation and litigation expenses awarded were a punitive measure intended to address the mental strain and financial instability caused by the bank’s inaction.
Proactive Measures for Banking Consumers
While the legal system is increasingly favorable toward the consumer in cases of proven banking deficiency, the best defense against financial fraud remains vigilance. The Delhi case succeeded largely because the account holder was able to provide documentary evidence, including an email timestamped shortly after the event and a police complaint. In the digital age, documenting every communication with a bank is essential. Should a transaction go wrong, the immediate filing of a police report and a formal written complaint to the bank’s nodal officer are mandatory steps to satisfy the “prompt reporting” criteria set by the RBI.
Furthermore, consumers must be aware of the “Limited Liability” window. Reporting an incident within three working days significantly increases the likelihood of a zero-liability outcome. Waiting weeks or months, as often happens when consumers are unaware of their rights, provides the bank with grounds to argue against a full refund. As financial technology continues to evolve, the digital literacy of the Indian population must keep pace. Consumers should utilize the various tools provided by banks, such as daily transaction limits, app-based blocking features, and opting out of international or online transaction capabilities for accounts that are not actively used for such purposes.
Conclusion: The Future of Digital Financial Security
The resolution of this case serves as a benchmark for consumer protection in the Indian banking industry. It reinforces the principle that digital convenience cannot come at the cost of consumer safety. For banks, the message is clear: the era of deflecting responsibility by blaming the customer for OTP leaks is over. Institutions must prioritize the security of their digital infrastructure and provide better, more reliable alert systems.
For the regulatory environment, this verdict encourages a more proactive approach to auditing bank security protocols. As the volume of electronic transactions in India continues to climb, the judicial system will likely see more cases of this nature. Moving forward, the integration of artificial intelligence for fraud detection and faster grievance redressal mechanisms within banks will be essential to maintaining trust in the digital economy. The triumph of the account holder in this case is a victory for digital accountability, ensuring that when the system fails, the entity responsible for that system bears the financial burden.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News