The Japanese government is set to unveil a comprehensive “emergency countermeasures package” on November 6, marking a decisive shift in its national strategy to combat a surge in sophisticated cyberattacks. The initiative follows a wave of security breaches that have resulted in widespread personal information leaks and significant financial losses across both the public and private sectors.
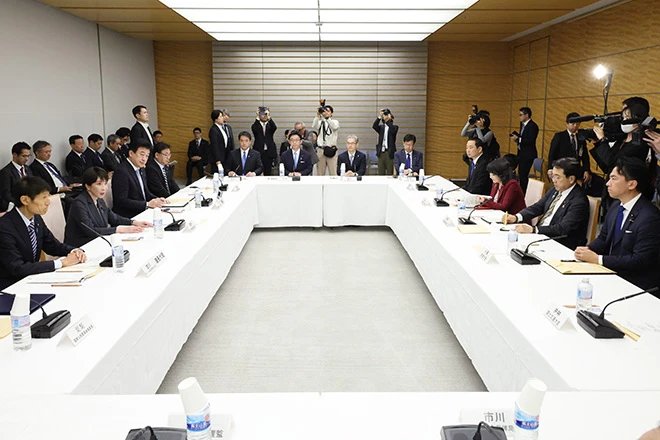
Prime Minister Sanae Takaichi, who initiated the effort during a ministerial panel meeting on October 26, has tasked her cabinet with constructing a robust defense framework. A dedicated Cabinet meeting of relevant ministers is scheduled to convene at the Prime Minister’s Office on November 6 to finalize and formalize the emergency measures.
Central to the government’s plan is the establishment of a “unified point of contact,” designed to streamline how companies report and respond to cyber incidents. By centralizing this process, the government hopes to provide businesses with more effective, real-time guidance during active threats. Furthermore, the package prioritizes the integration of artificial intelligence, which will be deployed to help private enterprises proactively identify and patch system vulnerabilities before they can be exploited by malicious actors.
The emergency package is expected to be multi-faceted, addressing critical infrastructure and human resource gaps. According to officials familiar with the discussions, the plan will focus on strengthening cross-ministerial systems for damage analysis and providing centralized consultation services. Recognizing that medical institutions have increasingly become prime targets, the proposal includes specific provisions to enhance cybersecurity standards within the healthcare sector. Additionally, the government is prioritizing the development and retention of specialized cybersecurity personnel, acknowledging that a skilled workforce is the most critical component of national digital security.
Perhaps the most aggressive aspect of the new strategy involves the expansion of “Active Cybersecurity Defense” (ACD) capabilities. Building on legislation revised in October, which authorized police and the Self-Defense Forces to access and disable an attacker’s infrastructure, the government is looking to scale up its operational capacity. The upcoming package will outline specific measures to secure the specialized personnel and resources necessary to implement these preemptive defense protocols.
“The threat landscape has evolved rapidly, and our defenses must evolve even faster,” a government official stated regarding the urgency of the announcement. By moving beyond passive observation toward a more proactive, offensive-capable stance, the administration hopes to deter attackers while providing a stronger safety net for victims.
As the November 6 deadline approaches, industries are watching closely to see how these government-led changes will reshape their own compliance and security requirements. The effort represents one of the most significant government interventions in national cybersecurity to date, signaling a new era of state-backed protection against digital threats.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News