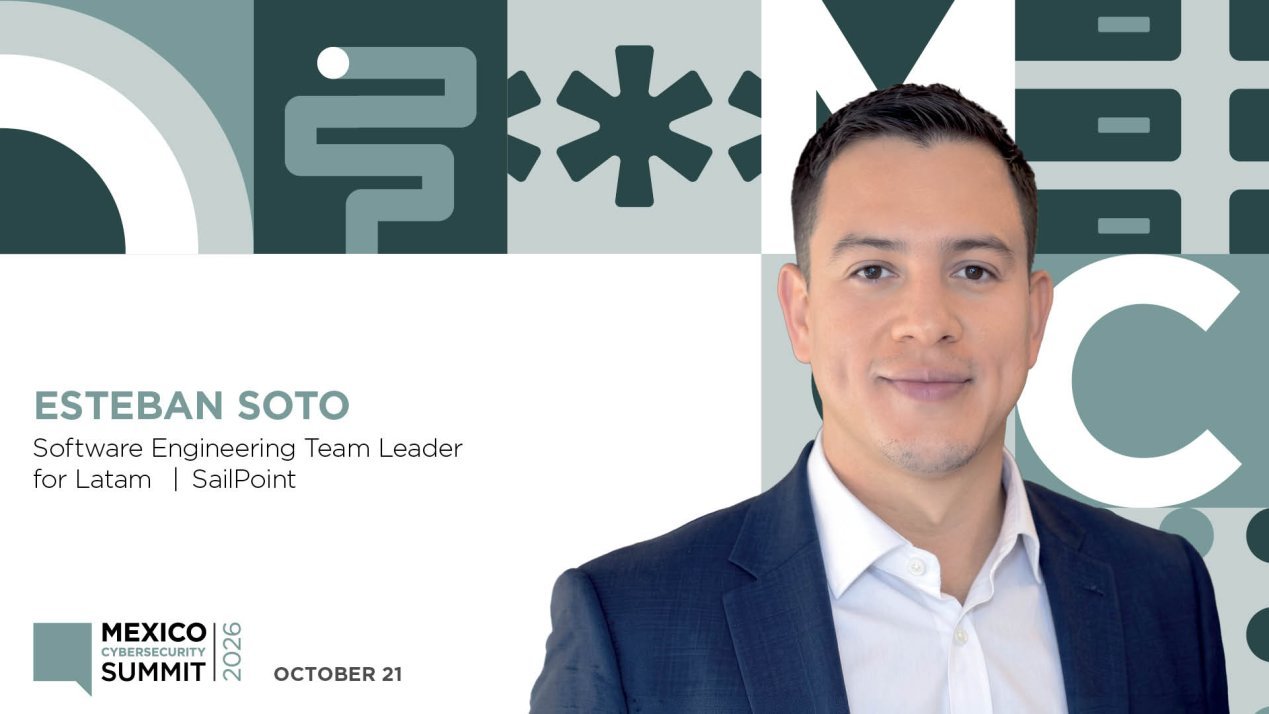
Apple is redefining the corporate security paradigm by shifting the focus from reactive software patches to proactive, hardware-embedded protections. During the recent Mexico Cybersecurity Summit 2026, industry experts emphasized that for the modern enterprise, the battle against cyber threats must begin at the chip level, effectively merging high-tier security with streamlined IT management.
## The Foundation: Security by Design
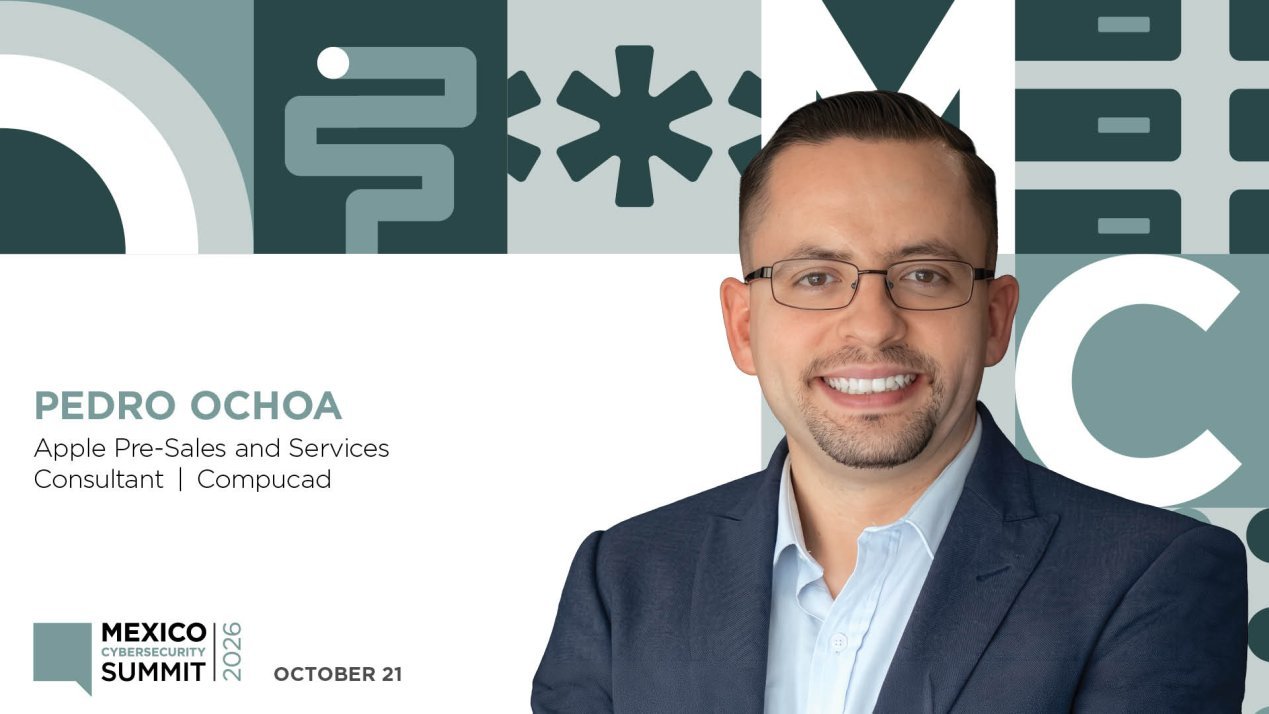
Modern enterprise environments are grappling with an increasingly complex threat landscape where traditional perimeter defenses are often insufficient. According to Pedro Ochoa, an Apple Pre-Sales and Services Consultant at Compucad, the core of Apple’s strategy is the integration of security directly into the hardware architecture.
This philosophy aligns with findings from an IDC study, which revealed that 72% of IT decision-makers prioritize security features that are built into the hardware, firmware, and operating system from the start. Rather than relying on third-party security software as an afterthought, Apple utilizes a “Secure Enclave.” This dedicated subsystem acts as a vault for biometric data and encryption keys, ensuring that sensitive information remains isolated from the rest of the system. By baking these protections into the silicon, organizations can ensure robust data integrity without compromising the user experience or forcing IT teams to manage cumbersome third-party security layers.
## Enforcing a Chain of Trust
Beyond the physical hardware, Apple leverages a secure boot process that serves as a fundamental pillar for enterprise compliance. This process establishes a “chain of trust” during the device startup, where each stage of the boot sequence verifies the integrity of the next before execution. This prevents unauthorized software or malicious code from embedding itself into the device’s core.
Furthermore, Apple’s use of a signed, read-only system volume restricts unauthorized changes to critical operating system files. Even administrators are prevented from modifying these segments, a feature that significantly reduces the attack surface for malware. This level of rigidity is a major advantage for companies that must meet strict regulatory standards, such as FIPS 140-2 and 140-3. By providing clear technical controls that map to these compliance frameworks, Apple enables IT departments to maintain uniform security postures across global fleets with minimal administrative overhead.
## Efficiency and Real-World Impact
The transition to a hardware-centric security model offers more than just protection; it provides a tangible return on investment through operational efficiency. A case study featuring the digital bank Inter illustrates the potential for organizations to scale their infrastructure without ballooning their IT budget.
After shifting to a Mac-standardized environment, the bank reported an 80% reduction in technical support tickets and successfully eliminated malware incidents entirely. By reducing the complexity of device management and decreasing the frequency of hardware repairs, Inter demonstrated that a robust, integrated security strategy can serve as a catalyst for business performance.
As organizations continue to navigate the demands of remote and hybrid work, the ability to secure thousands of endpoints through centralized management is no longer a luxury—it is a necessity. Apple’s approach proves that when security is treated as an architectural requirement rather than a software add-on, it empowers organizations to spend less time managing vulnerabilities and more time focusing on innovation. By embedding protection into the device itself, the future of enterprise cybersecurity is becoming increasingly automated, resilient, and invisible to the end user.
Disclaimer: This content is auto-generated for informational purposes only.
Source: Read Original News